

Role-scoped access
Shape permissions around a person’s role and operational scope.
Security and trust
Protect sensitive provider information with least-privilege access, role-aware authority, managed identity and traceable operational evidence.
Inclusify separates identity authentication from provider authority, then applies role, service scope, delegation and review requirements inside the workflow. Certifications and assurance reports are published only after formal verification.
Talk through your prioritiesAccess and identity
Identity, authority and data location should be visible architecture decisions, not vague platform promises.
Give each person only the access required for their current responsibility.
Resolve provider role, service scope and delegated authority after identity is confirmed.
AWS Asia Pacific (Sydney), region ap-southeast-2.
AWS Cognito for managed identity authentication at the sign-in boundary.
Support MFA and 2FA to add another verification factor for account access.
Two deliberate boundaries: Cognito confirms identity. Inclusify then resolves provider role, service scope and least-privilege authority.
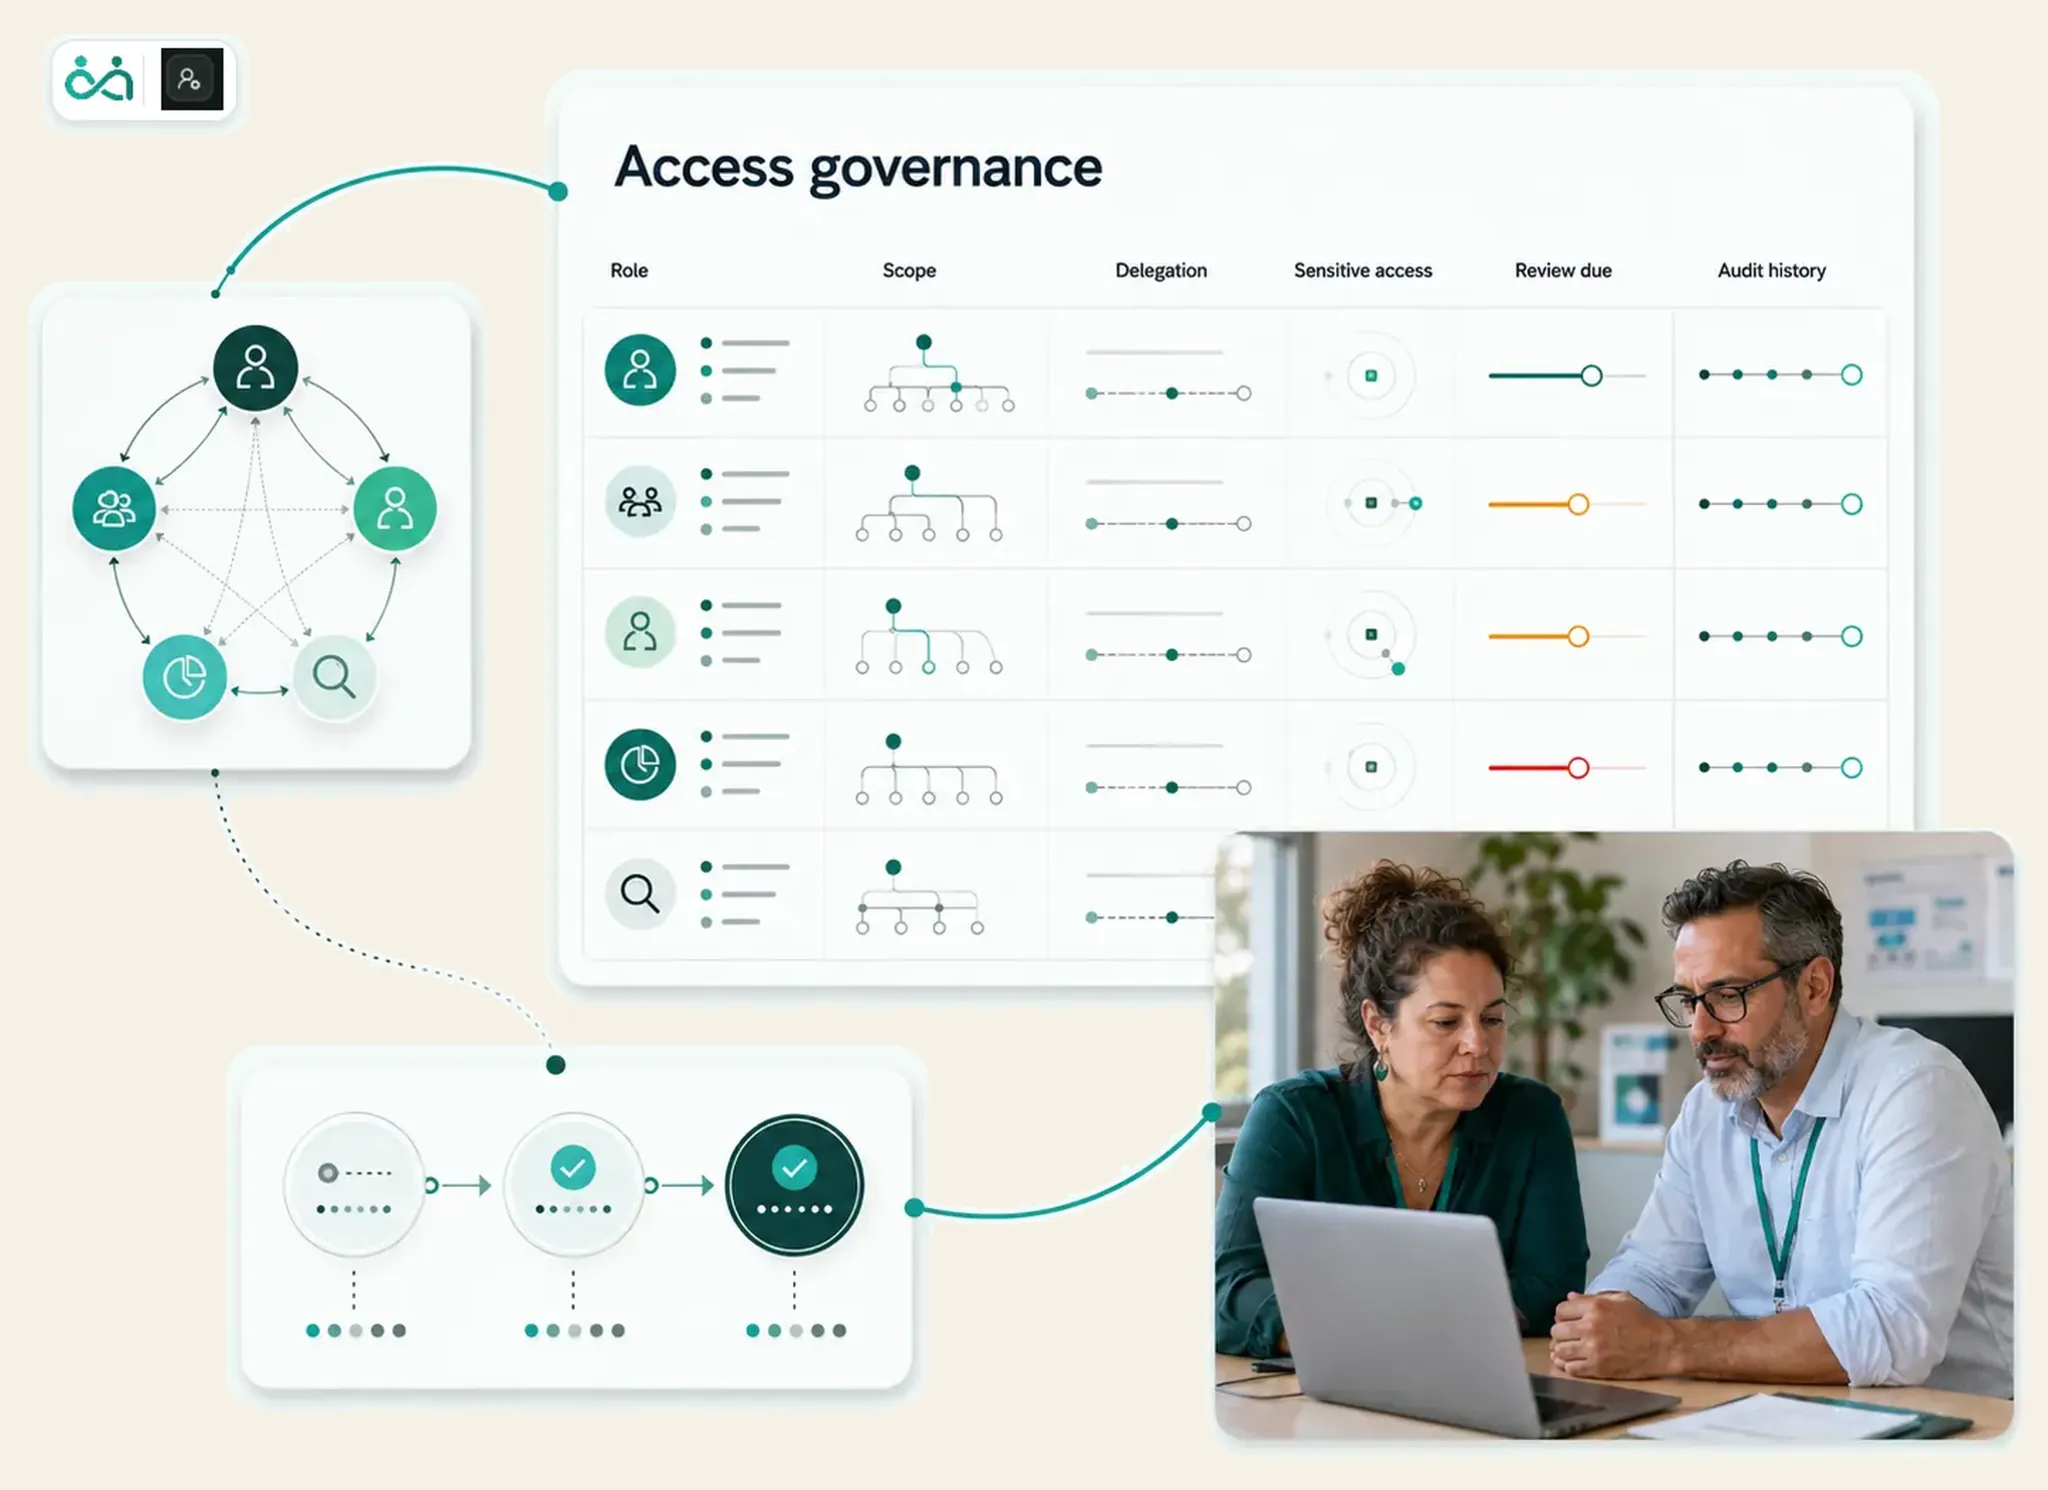
Connect role, scope, delegation, sensitive permissions and review dates.
Shape permissions around a person’s role and operational scope.
Keep important actions in context for review.
Use owners, due dates and review points.
Limit information to what the service requires.
Reduce unnecessary exposure of records.
Connect records to the decisions that produced them.
Next step
We will use it to understand your current pressure and show where a connected approach could help.
Book a walkthrough